


BIT's Core Network
Core Network
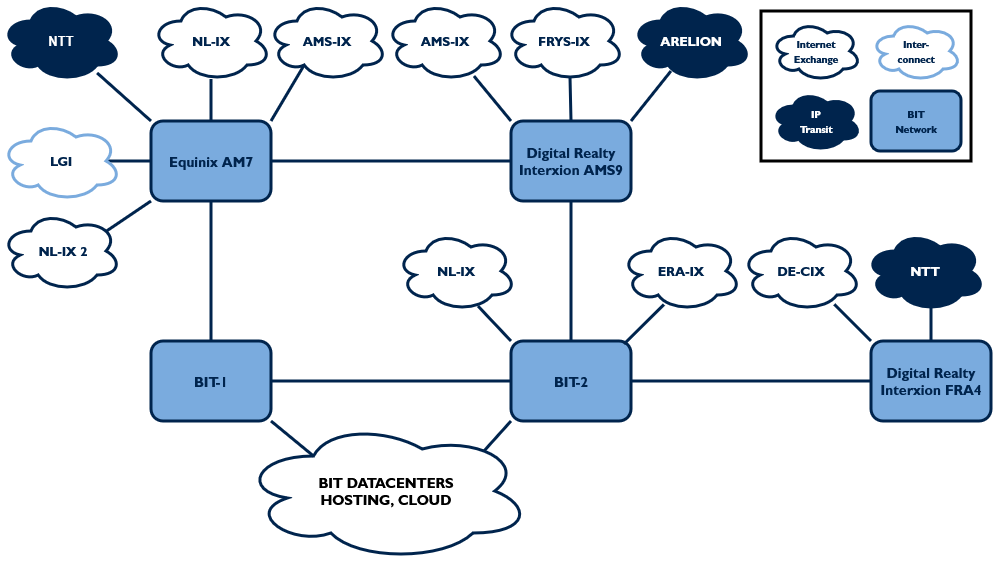
BIT operates a redundant core network connecting six locations. At the heart of the network is a fibre-optic ring connecting BIT-1 (Ede), BIT-2 (Ede) and two data centre locations in Amsterdam: Digital Realty (Interxion) and Equinix AM7. BIT also has a presence in Frankfurt (Interxion FRA4).
BIT rents rack space at the Amsterdam and Frankfurt locations, while BIT-1 and BIT-2 are wholly owned by BIT.
Redundantly Designed Fibre-Optic Infrastructure
The connections between BIT-1 and Equinix AM7, BIT-2 and Digital Realty, and between Equinix AM7 and Digital Realty have been deployed along geographically separate routes. Our agreement with the supplier ensures that this separation is maintained following any works, and that maintenance on these fibre-optic connections is never carried out simultaneously. This is designed to minimise the risk of multiple disruptions affecting our fibre-optic infrastructure at the same time.
The connection to Frankfurt deliberately bypasses Amsterdam, instead following an eastern route with a redundant path. As a result, outages in the Amsterdam region don’t affect the international connectivity of BIT’s network.
BIT uses DWDM technology (Dense Wavelength Division Multiplexing), which allows multiple wavelengths of light to be transmitted over the same fibre. This makes it straightforward to scale capacity as demand grows. BIT also provides wavelengths over DWDM as a service to customers, enabling dedicated capacity between locations.
BIT also provides protected VLANs between locations in the Netherlands, using redundant connections to ensure higher availability.
Through Equinix, BIT can also provide connectivity to other Equinix data centres in Amsterdam. This allows customers and partners to connect at additional locations in Amsterdam without requiring separate physical fibre deployments.
The network uses fast failover mechanisms: if a connection or router fails, traffic is automatically rerouted via an alternative path with virtually no interruption.
Peering, Transit and Private Interconnects
BIT’s network is designed around reachability, flexibility and reliability. To achieve this, BIT combines several forms of interconnectivity: IP transit, public peering and private interconnects. This combination ensures that multiple routes are always available to destinations across the internet.
For global connectivity, BIT uses multiple IP transit providers. These transit connections are distributed across different locations within the network, with each providing multiple alternative routes. This means BIT isn’t dependent on a single provider or route, helping to keep the network reachable even during outages or maintenance.
BIT also exchanges large volumes of traffic directly with other networks through Internet Exchanges. At these exchanges, traffic is exchanged without passing through a transit provider, resulting in lower latency and greater control over traffic flows. BIT operates an open peering policy and is connected to multiple Internet Exchanges in the Netherlands and Germany, including AMS-IX, NL-ix, ERA-IX, Frys-IX and DE-CIX. Connections are redundant and distributed across multiple geographically separate locations, avoiding a single point of failure.
In addition to public peering, BIT uses PNIs (Private Network Interconnects). These are dedicated connections between BIT’s network and another network, allowing routes to be exchanged directly over fixed, guaranteed capacity. PNIs are used where substantial volumes of traffic are exchanged with a specific network on an ongoing basis. One example is BIT’s interconnect with Liberty Global Inc. (LGI), which allows traffic to and from networks within the LGI group to be handled efficiently and predictably.
By combining IP transit, peering and private interconnects, BIT operates a scalable network with multiple paths to every destination. This provides high availability, stable performance and the flexibility to respond quickly to changing traffic patterns. BIT also uses automated DDoS detection and mitigation through NaWas, allowing attacks to be detected quickly and malicious traffic to be filtered automatically, protecting the availability of both the network and customer services.
Ready for Current and New Internet Standards
IPv6
BIT has supported IPv6 for more than 20 years and has long been at the forefront of its adoption in the Dutch market. BIT has consistently played a pioneering role in the implementation of IPv6 and actively shares its knowledge with customers and the wider industry.
IPv6 is available throughout BIT’s entire network and is supported across all services. The only exception is mobile internet, as Vodafone doesn’t support IPv6 on the service BIT uses to provide mobile connectivity.
At BIT, IPv6 isn’t treated as an afterthought: the same SLAs and availability commitments apply to IPv6 as they do to IPv4.
RPKI
BIT also uses RPKI (Resource Public Key Infrastructure). RPKI makes it possible to cryptographically specify which network is authorised to announce particular IP address blocks via BGP. This allows other networks to validate that routes genuinely originate from the authorised network.
This form of Route Origin Validation helps prevent a significant proportion of BGP hijacks and route leaks. BIT has created digital certificates for its own IP address ranges, explicitly authorising the BIT network to announce these addresses. In doing so, BIT actively contributes to a safer and more reliable internet.


